

- 1 JWTs ensure robust API security: JWT is tamper proof and helps to maintain data integrity because they are signed tokens.
- 2 JWTs provide scalability: Also, given that JWTs do not have a session, they do not require session storage, hence providing better scalability.
- 3 JWTs are versatile and user-friendly: It supports various authentication schemes and it is fairly simple to implement and has massive library support.
In the fast-paced world of custom software development, security is paramount. Whether you’re an Android app agency, an iOS app development services provider, or a business software development company, ensuring the safety of your API is crucial. That’s where JSON Web Tokens (JWTs) come into play. In this blog post, we’ll explore how to secure your Node.js API using JWTs and why they’re a favored choice in the realm of API development.
Why Choose JSON Web Tokens for Your API?
JWTs have gained immense popularity in the world of application development companies and software development services, and for good reason. Here are some compelling advantages of using JWTs for your API security:
- Security: JWTs are signed tokens, making them highly secure and tamper-proof. Any attempt to alter the token will result in invalidation, ensuring the integrity of your data.
- Statelessness: JWTs are self-contained, containing all the necessary user information. This means your server doesn’t need to store session data, making JWTs stateless and easily scalable.
- Flexibility: JWTs can be used to implement a wide range of authentication and authorization schemes, such as single sign-on (SSO) and OAuth 2.0, making them adaptable to various use cases.
- Simplicity: JWTs are user-friendly and straightforward to implement. Numerous libraries and frameworks are available for different programming languages and platforms, making integration a breeze.
JWT vs. Session-Based Authentication: Which Fits Your API?
Before going through the process of implementing JWTs, it’s a good idea to understand what we’re choosing between since, while it’s a viable replacement option, the alternative (session based authentication) is also completely valid in many scenarios.
With session based authentication, the server stores a representation of the session on the server (in memory or in a database) and returns a session id cookie to the client from which all requests will be verified. These types of sessions are straight forward both in their implementation (as supported natively by browsers) and verification, are simple to invalidate (deleting the session from the server) and grant immediate revocation of access once the session is deleted.
JWTs flip many of these tradeoffs. Because a JWT is self contained and signed, servers that verify it have to store nothing about the session in order to check it. This makes them much easier to scale as you don’t need to worry about having a shared session store between servers, but makes revoking permissions harder as it now requires additional infrastructure (such as a blacklist) to make sure expired tokens are no longer used.
For a Node API that’s serving mobile clients or other backends (as a common example of a single sign on situation for people using your app on both android and ios as per the intro to this guide, as a common example) this makes JWTs the obvious choice as there’s no shared session store between those platforms. On the other side, sessions are often easier to work with when you’re just building a single app (for example, a traditional server rendered website) that needs immediate revocation of permissions, they’re also likely the right choice. This isn’t an either/or situation and either solution is viable depending on the requirements for a given API.
Understanding JSON Web Tokens Components
JWTs consist of three essential parts:
- Header: Contains metadata about the token, such as its type and the signing algorithm used.
- Payload: Houses user-related claims, such as username, email, and role.
- Signature: Ensures the token’s authenticity and integrity.
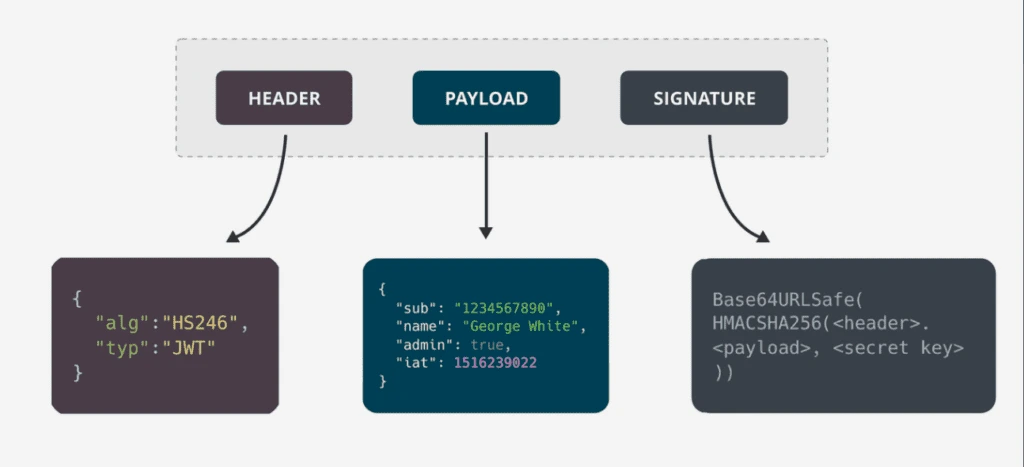
Common Vulnerabilities to Avoid When Implementing JWTs
JWTs may be secure by default; nevertheless, this does not imply that their implementation is not exposed towards attacks. Several common mistakes that occur during the implementation of JWTs should be highlighted.
The most apparent mistake is using a secret key that is too simple or predictable as it permits an attacker to brute-force the secret key and create a valid JWT with an arbitrary claims encoded. It is effective in practice since the secret key should be known only to the server that issued them, thus rendering the signed JWTs insecure. The secret key must be complex enough to avoid brute-force attacks and should not be placed in public repositories.
Algorithm confusion is another commonly occurring vulnerability that originates from an incorrect JWT library configuration. Specifically, the header of the JWT indicates the algorithm with which it was signed; this information is typically used by the server to verify the integrity of the JWT. If the verification code specifies the specific algorithm without checking that the JWT actually utilizes, then it will be relatively simple to manufacture a fake JWT. One example of such an attack refers to the change of the header’s algorithm to HS256, which is commonly used and trusted. Such type of attack is especially dangerous since the JWT will contain valid claims and will successfully pass the verification. To avoid such attacks, the code that verifies the JWT should check that it indeed specifies the expected algorithm.
Another mistake manifests in creating JWTs that are not expired or setting their expiration time to a very far date. In this case, the attacker can utilize the intercepted JWT indefinitely. To mitigate this vulnerability, the tokens should possess an appropriately set expiration time, which does not imply that they should not expire. On the contrary, there should be some time within which the user should continue the application after logging in. It can be resolved by utilizing a refresh token mechanism, which refers to a short-lived access token and a refresh token needed to obtain a new access token when it expires.
Finally, the last common mistake is choosing the wrong place to store the token on the client side. It is discussed in detail further in this section; therefore, it is essential to pay attention to the moment of implementing JWTs on the client side. Following the recommendations mentioned above will allow avoiding many potential vulnerabilities during the initial JWT setup.
To begin securing your Node.js API with JSON Web Tokens, follow these steps:
- Install the jsonwebtoken Package:
npm install jsonwebtoken- Create a Secret Key:
const SECRET_KEY = "my-secret-key";- Define a JWT Token Generation Function:
const generateJwtToken = (user) => {
  const payload = {
    id: user.id,
    username: user.username,
    email: user.email,
    role: user.role
  };

  const token = jwt.sign(payload, SECRET_KEY, {
    expiresIn: "1h"
  });

  return token;
};- Define a JWT Token Verification Function:
const verifyJwtToken = (token) => {
  try {
    const decodedToken = jwt.verify(token, SECRET_KEY);
    return decodedToken;
  } catch (error) {
    return null;
  }
};- Create a Middleware Function to Protect API Routes:
const protectRoute = (req, res, next) => {
  const authorizationHeader = req.headers["authorization"];
  if (!authorizationHeader) {
    return res.status(401).json({ message: "Unauthorized" });
  }
  const token = authorizationHeader.split(" ")[1];
  const decodedToken = verifyJwtToken(token);
  if (!decodedToken) {
    return res.status(401).json({ message: "Unauthorized" });
  }
  req.user = decodedToken;
  next();
};
- Utilize the protectRoute Middleware Function:
app.get("/api/protected", protectRoute, (req, res) => {
  // The user is authenticated and authorized, granting access to the protected resource.
  res.json({ message: "Welcome to the protected resource!" });
});
This example serves as a foundation for securing your Node.js API with JWTs. Depending on your requirements, you can further enhance your authentication system by implementing features like refresh token mechanisms or integrating user management systems to store user information.
Best Practices for Token Storage, Expiration, and Secret Management
Besides the questions of implementation discussed in this guide, there are also a few practices that are usually undertaken to make a production-grade JWT implementation secure.
Where the client stores the token is a question that requires careful consideration. The easiest place to save it is the browser’s local storage, but this practice creates a serious vulnerability if any cross-site scripting (XSS) attacks can read the token’s value. A safer option is to save the JWT in an HttpOnly cookie that is not accessible by browser JavaScript; however, the cookies might be subject to cross-site request forgery (CSRF) attacks.
The practice of rotating keys periodically also falls under the security best practices category. While it does involve some additional complexity, it is important to remember that any compromised signing key must be taken off of production servers immediately. It is better to have preparations for such a scenario, which involve some additional complexity, such as gracefully handling expired tokens.
The guide mentioned refresh tokens briefly when it discussed the possibility of sending tokens with every request. In practice, such tokens are often short-lived, and a separate refresh token is used to obtain new JWT instances. This way, even if an access token is stolen, it will expire soon, limiting the damage. Meanwhile, a client should use refresh tokens to get new access tokens when needed, and those tokens should be stored securely, perhaps on a server, where they can be revoked if compromised.
Finally, a production-grade JWT implementation should have logging and monitoring for failed requests. Failed token verification attempts can indicate that an attacker is trying to brute-force their way into a system by attempting to guess tokens. Having alerts for such activity can help mitigate damage by detecting attacks early enough.
How JWTs Fit Into a Broader API Security Strategy
Everything covered in this guide addresses one specific layer of API security — authentication and authorization — but it’s worth being clear that JWTs alone don’t make an API secure end to end. They’re one piece of a larger picture, and treating them as the whole solution is a common way projects end up with gaps despite having “done” authentication correctly.
HTTPS is the most basic requirement sitting underneath everything else here. A JWT sent over an unencrypted connection can be intercepted in transit regardless of how carefully it was generated or verified, which makes enforcing HTTPS across an entire API a prerequisite for JWT-based security to mean anything at all, not an optional extra.
Input validation matters just as much once a request is authenticated as before. A valid JWT proves who’s making a request, not that the data in that request is safe to use. An authenticated user sending malformed or malicious input can still cause problems — from corrupted data to injection attacks — if the API trusts the request body just because the token attached to it checked out. Authentication and input validation are separate concerns that both need to be handled, not substitutes for each other.
Rate limiting is worth mentioning too, particularly on authentication endpoints themselves. Login routes are a common target for brute-force attempts, and a well-implemented JWT system can still be undermined if an attacker is free to make unlimited login attempts while guessing at credentials. Limiting how many requests a single IP address or account can make in a given window is a standard, relatively simple addition that closes off a real attack path.
None of this diminishes what JWTs bring to a Node.js API — the security, statelessness, and flexibility described throughout this guide are genuine advantages. It’s simply a reminder that they’re one well-chosen tool within a wider security approach, not a replacement for the other fundamentals an API needs regardless of how it handles authentication.
In Conclusion
JSON Web Tokens (JWTs) are a formidable ally when it comes to securing your Node.js API. Their robust security, statelessness, flexibility, and simplicity make them a preferred choice among Android app agencies, iOS development services providers, and custom software development companies alike. Furthermore, the extensive developer community and abundant support resources for JWTs make them a reliable option for your API security needs.
Whether you’re in need of cross-platform app development services, healthcare custom software development, or banking software development, implementing JWT-based security can help safeguard your data and ensure smooth operations in your custom software development journey. So, when it comes to securing your Node.js API, consider JWTs as a top-notch choice for achieving peace of mind and robust protection.
Getting real value out of JWTs, though, depends on more than just adding the jsonwebtoken package and wiring up a basic middleware function, as covered in the implementation steps earlier in this guide. It depends on the details discussed throughout this piece — choosing a strong, properly managed secret key, setting sensible expiration times, storing tokens safely on the client, and treating JWTs as one part of a broader security approach rather than the entire solution on their own. Skipping any of these doesn’t necessarily break the implementation outright, but it does leave gaps that tend to surface later, often at the worst possible time.
The good news is that none of this requires reinventing anything. Every practice described here — refresh tokens, HTTP-only cookie storage, rate limiting on authentication endpoints, explicit algorithm verification — is well established and well documented, with mature libraries available for Node.js that handle most of the hard parts. The work is mainly in taking the time to apply these practices deliberately rather than stopping at the minimum implementation.
Whether you’re building for cross-platform app development, healthcare custom software, or banking software development, implementing JWT-based security thoughtfully — not just technically correctly — can help safeguard your data and support smooth, reliable operations throughout your custom software development journey. When it comes to securing a Node.js API, JWTs remain a genuinely strong choice, provided the surrounding practices are given the same attention as the token itself.