

Regulated enterprises are favoring boutique, senior-heavy delivery pods over Big Four vendors. It’s not that large vendors are unsafe, but purely based on the delivery characteristics of the task at hand, scale doesn’t equal depth of compliance expertise or speed. Boutique pods can tie access controls, auditing logging, and encryption directly to their regulatory framework; offer direct access to engineers; and apply audit findings directy, circumventing change-management processes that are sized to support much larger organizations. Big vendors are still a good choice for genuinely massive, multi-year enterprise programs. Most regulated software work falls somewhere in between and should evaluate both categories against the same criteria: documented framework experience, audit-ready documentation, and a rehearsed incident response process, and let the evidence speak for itself.
- 1 Vendor size doesn't guarantee compliance expertise; that team on your project might not know your regulatory framework very well.
- 2 Large-vendor bureaucracy can slow the urgent changes compliance and security issues often require, the opposite of what that process was meant to protect.
- 3 Generic, enterprise-wide playbooks often miss the specific nuances of a narrower framework or a particular regulator's expectations.
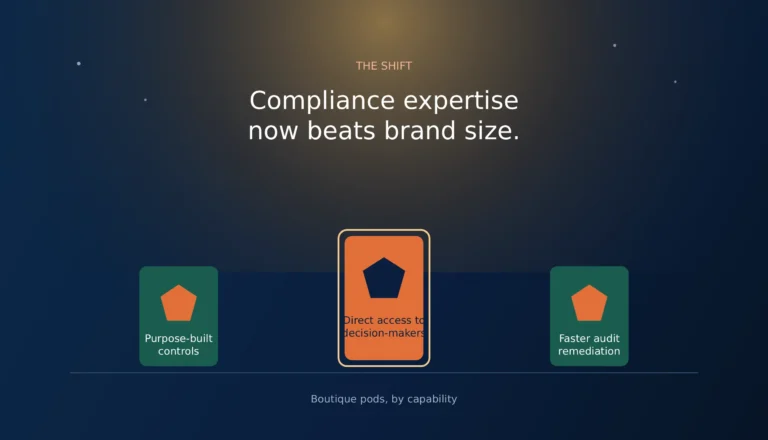
- 4 Boutique pods offer purpose-built controls - access, audit logging, and encryption that map directly to your framework rather than generic policy.
- 5 Direct access to the engineers doing the work resolves compliance questions faster than routing through account management layers.
Regulated industries were long assumed to be the exclusive territory of large, established IT vendors, the perceived safety of scale mattered more than agility. That assumption is shifting, as more regulated businesses look for delivery models that combine compliance rigor with real speed.
Part of this shift comes from experience: many regulated companies have now worked with a large vendor at least once, and have seen firsthand that scale doesn’t automatically translate into either compliance expertise or delivery speed.
The shift is also generational. Newer compliance and engineering leaders inside regulated companies increasingly evaluate vendors on demonstrated expertise rather than brand recognition alone, opening real space for smaller, more specialized firms to compete for this work.
None of this means large vendors are the wrong choice for every regulated engagement; for genuinely massive, multi-year enterprise programs, their scale can be a real advantage. The shift is narrower and more specific: for a growing share of regulated software projects, boutique teams are proving to be the better fit, not the riskier one.
At Innostax, we’ve seen this shift firsthand working with regulated clients who need both — and increasingly, AI-native managed engineering pods for SaaS founders , senior-heavy teams that own delivery and are built for quick turnaround are proving to be a better fit than expected.
Why “Big Vendor = Safe Choice” Is Being Reconsidered
Scale Doesn’t Guarantee Compliance Expertise
A large vendor’s overall scale doesn’t necessarily mean the specific team assigned to your project has deep expertise in your particular regulatory framework.
Bureaucracy Can Slow Compliance Work Too
Ironically, the same layered process that’s supposed to add safety at large vendors can also slow down the urgent fixes that compliance and security issues often require.
Generic Playbooks Don’t Fit Every Framework
Large vendors often apply a broad, standardized compliance playbook across many clients, which can miss the specific nuances of a narrower framework or a particular regulator’s expectations.
How Regulatory Frameworks Differ in What They Actually Demand
Compliance isn’t one thing, which is exactly why a standardized playbook struggles across frameworks. HIPAA is largely concerned with who can access protected health information and under what conditions, with a heavy emphasis on audit trails for access, not necessarily on how the software is built. SOC 2 cares more about the operational maturity of the organization delivering the software: change management, incident response, vendor risk management, over and above any single technical control. GDPR introduces obligations that have almost no equivalent in the other two, like the right to erasure, which has real architectural implications for any system that wasn’t designed with deletion in mind from the start.
A team that has only ever built against one of these frameworks and applies the same checklist to the next client’s different framework isn’t being thorough. They’re pattern-matching against the wrong pattern. The frameworks share a general spirit of accountability and control, but the specific technical and procedural requirements diverge enough that experience in one doesn’t automatically transfer to competence in another.
Compliance Ownership Can Get Diluted
In a large vendor engagement, compliance responsibility is sometimes spread across multiple internal teams, which can make it unclear exactly who is accountable when a specific control needs attention.
What Boutique Pods Can Offer Regulated Buyers
Purpose-Built Compliance Controls
A smaller, senior team can implement access controls, audit logging, and encryption standards mapped precisely to a specific framework, rather than relying on generic enterprise-wide policies.
Direct Access to Decision-Makers
Compliance questions can be resolved through direct conversation with the engineers actually doing the work, rather than routed through account management layers.
What Changes When Compliance Ownership Sits With One Team
Diluted ownership doesn’t usually fail loudly. It fails through small delays that compound: a finding gets logged, gets assigned to a team that also owns four other priorities, and sits in a queue behind work that has a more visible internal champion. Nobody is negligent. The structure just doesn’t have a single point of accountability for compliance-specific work, so it competes for attention against everything else on a larger team’s roadmap.
When one senior team owns both the delivery and the compliance posture of what they’ve built, a finding doesn’t need to be re-explained to a different group before someone can act on it. The person who gets the finding already understands the system it applies to, which removes an entire translation step that, in a larger vendor structure, often takes longer than the actual fix.
Faster Turnaround on Audit Findings
When an audit surfaces a finding that needs remediation, a smaller, senior team can typically move on it immediately, rather than routing the fix through a change-management process built for much larger organizations.
What to Verify Before Trusting a Boutique Firm With Regulated Work
Documented Compliance Experience
Ask for specific examples of frameworks the team has built against before HIPAA, GDPR, SOC 2 , not just a general claim of “security-first” development.
Audit-Ready Documentation Practices
A firm should be able to describe, concretely, how their development process generates the documentation an auditor would actually need to see.
A Clear Incident Response Process
Ask what happens if a security or compliance issue is discovered mid-engagement, a boutique firm with real regulated-industry experience should have a concrete, rehearsed answer, not an improvised one.
Questions That Separate Real Compliance Experience From Marketing Language
Most vendors, whether boutique or enterprise, will be able to recite a vague competence in compliance in a sales meeting. The goal of asking pointed questions is to elicit a generic answer.
“Walking me through how you would handle a data subject access request under the GDPR in the codebase we’re building.” A compliance-focused organization will give me specifics about the dataflows, but a team that only has theoretical knowledge will give me a breezy statement regarding their values.
“What was the most recent audit finding your team had to remediate, and how long did the remediation take?” Less prepared teams, or teams that haven’t actually done remediation, will have a sanitized or hypothetical response, as there is less reason for them to have a detailed, re-tellable response to the question.
“Who on the team has actually sat in on an audit?” Compliance knowledge that is solely theoretical doesn’t translate to the real-world constraints of an actual audit, which can involve a healthy dose of political acumen beyond the technical aspects.
The answers to these questions don’t have right or wrong answers, but can help identify if the prospective hire’s answers are informed by a particular project, or if they’re just espousing their company’s default response to compliance.
Building a Balanced Vendor Shortlist
Don’t Rule Out Either Category by Default
The right approach isn’t to categorically prefer boutique firms over large vendors, or vice versa, it’s to evaluate both against the same specific compliance and delivery criteria, and let the evidence decide.
Weight References From Similar Regulatory Contexts Most Heavily
A reference from a company in a genuinely comparable regulatory situation is worth far more than a longer list of references from unrelated industries, regardless of which size of vendor is being considered.
Regulated Doesn’t Have to Mean Slow
The choice between compliance rigor and delivery speed is increasingly a false one. The right boutique team, with genuine compliance expertise, can offer both often more effectively than a large vendor whose scale doesn’t translate into speed.
For regulated buyers willing to look past brand recognition, the actual due diligence question is straightforward: can this team show specific, verifiable compliance experience relevant to our framework? When the answer is yes, size stops being the deciding factor.
As more regulated companies share this experience with their peers, the assumption that only large vendors can be trusted with compliance-sensitive work is likely to keep eroding not because the risks have changed, but because the evidence about who actually manages them well has.
Organizations getting this right aren’t taking on more risk by choosing a boutique partner, they’re simply being more precise about what reduces risk, rather than defaulting to whichever vendor is largest.
The Hidden Cost of Vendor Switching in Regulated Environments
Switching vendors in the middle of a partnership is always expensive, but in a regulated industry the expense is non-obvious: institutional knowledge about how and why a particular control was implemented moves out with the team, and a new vendor gets the code and documentation but not the reasons for decisions an auditor might ask about eighteen months later.
This is part of why the vendor-size assumption has been so persistent. The decision to switch away from a large, established vendor has historically seemed riskier than staying put (even as the relationship sours) because the cost of re-explaining a compliance history to a new team outweighed the cost of their slow turn time. This logic only holds if the alternative to a large vendor is another one who will have to relearn everything from scratch; a boutique pod that documents their reasoning as they go, not just their output, reduces the cost of future switches being necessary and thus changes the math for choosing them in the first place.
Navigating Compliance Requirements and Need to Move Fast?
At Innostax, we build compliance-ready software with senior, accountable teams — without the delivery delays of a large vendor’s layered process.